The most important fact about the recent attacks on South Korean financial institutions is easy to miss beneath the AI headlines: the attackers did not break the core banking systems. They found weaker doors nearby.
Beginning around September 30, a coordinated campaign targeted internet-facing services used by loan solicitors, employees, contractors, and corporate customers. At least seven banks and financial firms reported compromises, while several others detected and blocked related probes. More than 68,000 people were reportedly affected, with exposed data ranging from names and phone numbers to annual income, borrowing limits, resident registration numbers, and Connecting Information codes used to identify people across South Korean online services.
Investigators found artifacts associated with ARTEX, an open-source, multi-agent penetration-testing framework. ARTEX can connect a large language model to a planner-and-worker architecture that performs reconnaissance, tests endpoints, interprets responses, and revises its approach. The evidence supports concern that attackers used AI-assisted tooling. It does not establish that an autonomous system independently selected the banks, initiated the operation, or operated without human direction. Nor does the Chinese origin of ARTEX establish the identity or nationality of the attackers. Open-source code can be used by anyone.
Those qualifications sharpen the real lesson. The campaign appears to have combined familiar weaknesses—under-protected auxiliary applications, weak authentication, insufficient rate controls, and excessive data access—with automation capable of adapting faster than a conventional script. AI did not repeal the fundamentals of security. It made every neglected fundamental easier to find and exploit at scale.
The attackers went around the fortified center
Financial institutions typically put their strongest controls around core ledgers, payment systems, and consumer banking applications. Those systems receive executive attention, regulatory scrutiny, penetration testing, fraud monitoring, and substantial engineering investment. The surrounding estate is often more uneven.
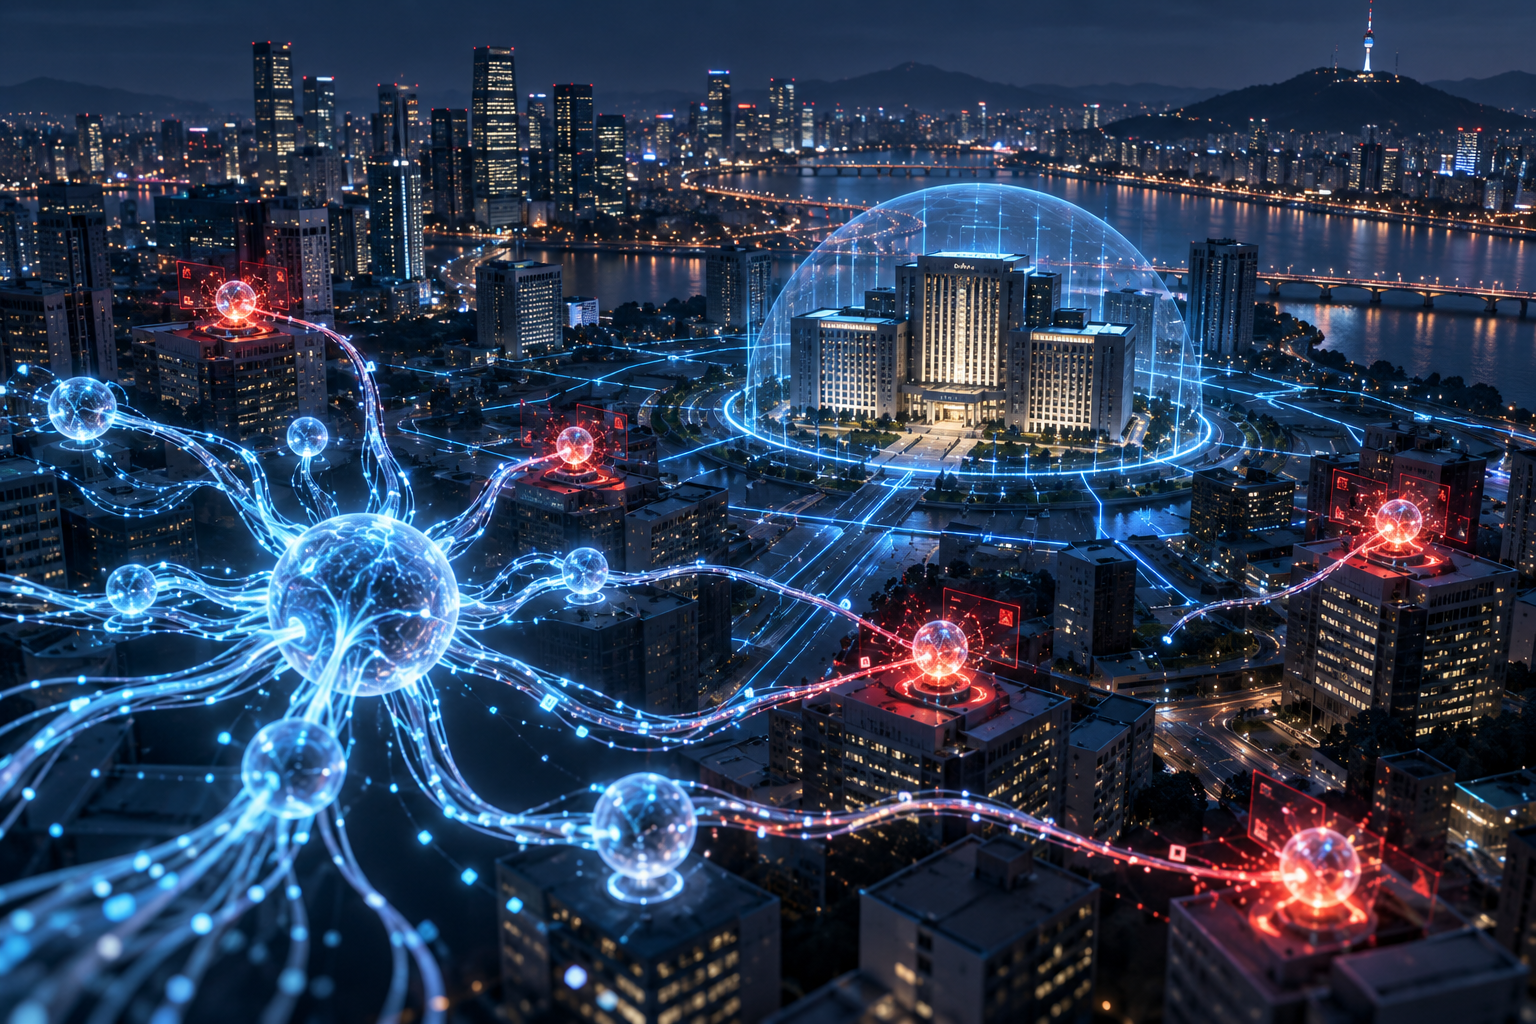
The South Korean campaign concentrated on that surrounding estate. Shinhan Bank’s affected service was reportedly a mobile inquiry application for outsourced loan solicitors. KB Kookmin Bank identified a compromise involving a mobile business-support system for employees. Hana Bank isolated a sales-support system. Hyundai Capital’s affected entry point served mortgage-loan solicitors. BNK Busan Bank reported exposure through a mobile sales-support system used by internal or outsourced personnel.
These systems were operationally important, yet they were separate from the institutions’ core banking platforms. That distinction helped contain direct financial damage, but it also reveals a governance problem. Organizations often classify an application according to its intended audience rather than the sensitivity of the data and actions available through it. A portal labeled “employee support” or “loan-agent inquiry” can still expose highly sensitive customer information. If the portal is reachable from the internet, it is part of the external attack surface regardless of the words on its architecture diagram.
The affected services reportedly lacked some combination of strong multi-factor authentication, robust session validation, granular authorization, and effective query-rate controls. Attackers could probe an interface, submit candidate identifiers, recognize a valid response, and then reuse the confirmed identifier across adjacent inquiry services. Each individual query might resemble an ordinary business transaction. Repetition and correlation transformed those ordinary queries into systematic data extraction.
The campaign therefore resembles an identity and application-logic failure more than a cinematic breach of a bank vault. The attacker did not need to defeat every defensive layer. The attacker needed one reachable workflow that answered too many questions for an insufficiently verified user.
The data exposure also carries consequences beyond the initial incident. Names and phone numbers already support basic phishing. Adding income, loan eligibility, application status, resident registration data, or a persistent digital identity code enables far more convincing fraud. A criminal impersonating a bank representative can cite information that only the bank and customer would be expected to know. Generative voice tools can industrialize that personalization, but the underlying danger comes from the quality and combination of the stolen data.
ARTEX changes the tempo of exploitation
Traditional automated attack tools follow deterministic instructions. A script sends a request, looks for an expected response, and continues along a predefined branch. Scripts are fast and scalable, but brittle. A changed field name, an unexpected error, a different page structure, or a defensive challenge can stop the workflow unless a human updates the code.
ARTEX represents a different operating model. The open-source framework uses a planner-and-worker pattern. A planner analyzes the available information and constructs an attack path. Concurrent workers execute delegated tasks, return observations, and allow the planner to revise the next step. The framework is an orchestration layer rather than a foundational AI model; an operator connects it to an external large language model through an application programming interface.
That architecture gives automation a limited form of semantic adaptability. A worker can return an error response or unfamiliar page structure, and the planner can interpret what happened rather than simply comparing the response with a fixed string. The system can alter parameters, try a related endpoint, or assign a new task. Human penetration testers have always adapted in this way. Agentic tooling compresses the observation-and-revision loop and allows more of those loops to run concurrently.
The distinction between autonomous selection and autonomous execution is essential. Available reporting does not show that ARTEX independently chose South Korean banks as targets or formed a criminal objective. A human operator could define the targets, provide credentials or infrastructure, remove approval gates, and allow the framework to automate portions of the operation. Describing that arrangement as “AI-assisted” is more accurate than implying that a rogue intelligence decided to attack a national financial system.
ARTEX was developed as a penetration-testing tool and includes human-approval safeguards in its ethical configuration. Its reported misuse illustrates the limits of code-level declarations once an offensive framework is published. An attacker with the source can alter or remove approval checks. The developer’s intent remains relevant when evaluating the project, but it does not constrain a malicious fork.
The operational advantage comes from the combination of adaptability and scale. A conventional credential-stuffing tool can make enormous numbers of requests. A human operator can interpret unfamiliar responses and improvise. An agent framework can bring some of that interpretation into the automated loop while coordinating multiple workers. The result is not omniscient hacking. It is faster exploration of mundane weaknesses across a broad target set.
South Korean investigators reportedly traced attack activity through dozens of IP addresses distributed across countries including the United States, Japan, Germany, Hong Kong, Thailand, and Vietnam. Distributed infrastructure can dilute obvious patterns, defeat simple geographic blocking, and slow attribution. It does not prove that the operators lived in any of those places. Rented servers, compromised hosts, and proxy services routinely separate an attacker’s location from the infrastructure visible to defenders.
This is why the discovery of Chinese-language ARTEX strings cannot carry an attribution claim by itself. Tool provenance, operator identity, infrastructure location, and sponsor are separate questions. Conflating them produces confident headlines and poor intelligence.
Static controls face an adaptive workload
The campaign exposes a growing mismatch between adaptive offensive tooling and defenses built around fixed indicators. Signature detection remains valuable. Known malicious addresses, payloads, and exploitation patterns should still be blocked. Static controls become less reliable when defenders treat them as the entire system.
An adaptive agent can vary request timing, headers, navigation paths, and parameters. If one endpoint produces a defensive response, the agent can try another route. If a request format changes, the system may be able to interpret the error and correct the request. None of these capabilities makes the agent invisible. They reduce the value of assuming that malicious automation will repeat one unmistakable pattern until a Web Application Firewall blocks it.
Behavior provides a more durable signal. Consider a loan solicitor who normally looks up a small number of assigned customers during business hours. If the same identity begins querying hundreds of unrelated records overnight, a valid password and an allowed IP address should not neutralize the anomaly. The system should evaluate the identity, device, workload, requested records, rate, sequence, and business relationship together. It should then restrict or terminate the session when the combined behavior no longer matches the authorized purpose.
This is an application of Zero Trust architecture, not a demand to purchase a product labeled “AI security.” Zero Trust requires explicit verification, least-privilege authorization, and the assumption that a session or network segment may already be compromised. For an auxiliary financial portal, those principles translate into concrete engineering decisions:
- Require phishing-resistant authentication such as FIDO2/WebAuthn for privileged and remote access where practical, with well-governed alternatives where deployment constraints remain.
- Authorize every query against the user’s current role, assignment, and customer relationship rather than granting broad lookup access after login.
- Apply per-identity, per-device, per-record, and aggregate rate limits so rotating an IP address does not reset every control.
- Use short-lived sessions and revoke them when behavior, privileges, or risk conditions change.
- Minimize each response to the fields required for the task instead of returning a complete customer profile for convenience.
- Detect enumeration through response patterns, failed identifiers, sequential searches, cross-endpoint correlation, and unusual result volumes.
- Preserve tamper-resistant authentication and access logs while keeping tokens and sensitive personal data out of the logs themselves.
Rate limiting deserves special attention because simple implementations are easy to evade. A limit attached only to a source IP fails when workers rotate through distributed infrastructure. A limit attached only to a user account fails when attackers possess multiple accounts or tokens. Useful controls combine multiple dimensions and impose limits at both the individual service and business-workflow levels. A customer-information platform should recognize that 50 requests spread across five “simple inquiry” endpoints may represent one enumeration campaign.
Data minimization reduces the value of every successful query. A loan-status screen may need to show whether an application can proceed without displaying a full resident registration number, annual income, personal address, and universal identity code in the same response. Masking, purpose-specific views, field-level authorization, and retention limits constrain the blast radius when authentication or application logic fails.
The AI supply chain expands the same trust problem
The supplied research also raises the Model Context Protocol (MCP), an open standard for connecting AI applications with tools and data. MCP was not confirmed as an ingress vector in the South Korean breaches. Treating it as part of the incident’s established forensic chain would overstate the available evidence.
MCP is still relevant to the strategic risk exposed by the campaign. Financial institutions are connecting models to document repositories, customer workflows, developer tools, and internal services. Every connection introduces credentials, authorization decisions, tool definitions, and data flows. If an AI assistant can retrieve a loan record or invoke a workflow, the assistant and its integration layer become part of the protected system.
The research describes GHSA-qx49-fqc8-xw99, a high-severity OAuth credential-theft vulnerability in the MCP Python software development kit. The official maintainer advisory assigns it no CVE. The issue affects SDK versions 1.9.1 through 1.29.1 and 2.0.0 through 2.1.1; versions 1.30.0 and 2.2.0 contain the fixes. A malicious or compromised MCP server could direct a vulnerable client to an attacker-controlled token endpoint and capture secrets or authorization material. Whether or not that vulnerability played any role in South Korea, the failure mode is instructive: an AI integration can become an identity conduit. Compromising the conduit may give an attacker the permissions of the connected service without requiring a frontal attack on the underlying database.
Organizations should manage agent connections as privileged machine identities. Each agent needs a defined owner, purpose, data classification, allowed tools, credential lifetime, and revocation path. Credentials should be short-lived and narrowly scoped. Tool calls should be authorized server-side, because a model’s instruction or intent is never an access-control decision. Sensitive actions should require step-up authorization or human approval based on impact, not on how confidently the model requests them.
The same inventory discipline required for legacy auxiliary portals applies to AI integrations. Security teams need to know which models, agents, MCP servers, software development kits, plugins, and external services can reach regulated data. They also need dependency monitoring and a response process capable of revoking affected credentials quickly. Adding an AI label does not create a new exception to established identity and supply-chain controls.
South Korea’s network-separation dilemma
The breaches arrived during a consequential policy transition. South Korea has long required strict separation between internal financial networks and the public internet. The rules protected core systems from direct exposure, but they also constrained the adoption of cloud services, software-as-a-service platforms, and generative AI systems that depend on external connectivity.
The Financial Services Commission had begun relaxing those restrictions through controlled exemptions. A second phase was scheduled to expand eligibility to smaller institutions on October 7. The government suspended that expansion as the breaches came to light.
The pause reflects a real design tension, but an air gap and modernization are not opposite security strategies. Network separation can reduce exposure for selected assets. It cannot compensate for weak identity, excessive authorization, or poorly governed applications that must remain online. Conversely, connecting more systems to cloud and AI services without first establishing a complete asset inventory and consistent controls creates new paths to the data.
Several reportedly affected firms had participated in the first phase of exemptions intended for institutions with stronger security capabilities. If confirmed through the continuing investigations, that detail suggests that institutional readiness assessments were too focused on core systems or planned AI environments. Readiness has to include the neglected portals, vendors, contractor pathways, and data interfaces already reachable from the internet.
The regulatory response moved in that direction. Authorities ordered inventories of internet-facing assets, authentication hardening, emergency vulnerability reviews, and rapid distribution of malicious infrastructure indicators across hundreds of financial firms. Those actions address the immediate campaign. Long-term resilience will depend on making the inventory continuous, enforcing uniform minimum controls, and measuring whether each exposed service can justify its access to sensitive data.
The incident also exposed the cost of fragmented response. South Korean cybersecurity responsibilities are divided among agencies responsible for national intelligence, the private internet ecosystem, and financial security. Specialized ownership has benefits, but machine-speed campaigns punish slow coordination. An indicator discovered at one institution can become actionable protection for every peer only if legal authority, technical formats, and operational processes support rapid sharing before the next institution is probed.
A practical defensive agenda
Behavioral models can correlate activity across identities, devices, endpoints, and time, while automated containment can reduce the interval between detection and token revocation. Those capabilities still depend on reliable signals and decisive controls. A model cannot enforce least privilege that was never designed, inventory an undocumented portal, or remove unnecessary fields from an API response. Defensive AI can improve analysis and response; it cannot substitute for architecture and governance.
A credible program begins with the full external attack surface. Every internet-reachable hostname, application programming interface, mobile backend, vendor portal, test environment, and remote administration path needs an owner, data classification, authentication standard, patch process, and retirement date. Discovery must be continuous because cloud services and development teams can create new exposure faster than an annual audit can record it.
Identity controls should be evaluated at the workflow level. Security teams should ask which customers an authenticated user may view, which fields appear, whether bulk activity has a legitimate purpose, and how quickly authorization can be withdrawn. Service accounts and AI agents require the same scrutiny as people.
Detection engineering should model abuse cases rather than collect logs without a decision path. Teams can test concrete scenarios: identifier enumeration across adjacent endpoints, one account shifting between countries, many accounts converging on the same records, unusual access outside business hours, or a contractor role retrieving customers outside its assignment. Each scenario needs a response—challenge, throttle, restrict, revoke, or escalate—and a way to preserve evidence.
Third parties must be inside the security boundary in governance terms even when they remain outside the corporate network. Contracts should define authentication, logging, incident notification, data minimization, and access-review requirements. Technically, outsourced personnel should receive individual, time-bound identities with narrow assignments. Shared credentials and broad “partner” roles turn one compromised user into a reusable extraction channel.
Finally, organizations need exercises that assume the attacker can adapt. A red-team test should not stop after confirming that a Web Application Firewall blocks a known payload. It should explore alternate endpoints, valid-but-abusive workflows, token theft, contractor access, and data aggregation across services. Defenders should practice containing a campaign while it changes behavior, rotates infrastructure, and targets several business units at once.
The South Korean breaches did not make established security engineering obsolete. They made incomplete security engineering more expensive. Strong authentication, least privilege, data minimization, asset inventory, behavioral monitoring, and rapid coordination were necessary before agentic attack tools appeared. Adaptive automation now gives adversaries a faster way to locate every place those controls were treated as optional.
That is the durable lesson for financial institutions and other critical infrastructure operators. The strongest system cannot define the organization’s security posture by itself. The posture is defined by the least governed service that still knows something valuable.
Sources
This article was developed from the supplied research report, Analysis of the October 2026 AI-Driven Cyberattacks on South Korean Financial Infrastructure. The report draws on coverage and technical material including: