The ConnectWise Cloud Backup compromise did not begin with malware on a customer endpoint. It did not depend on an unpatched server inside each victim organization. It did not even require an attacker to defeat multi-factor authentication one tenant at a time.
The attack began with trust that customers had already granted.
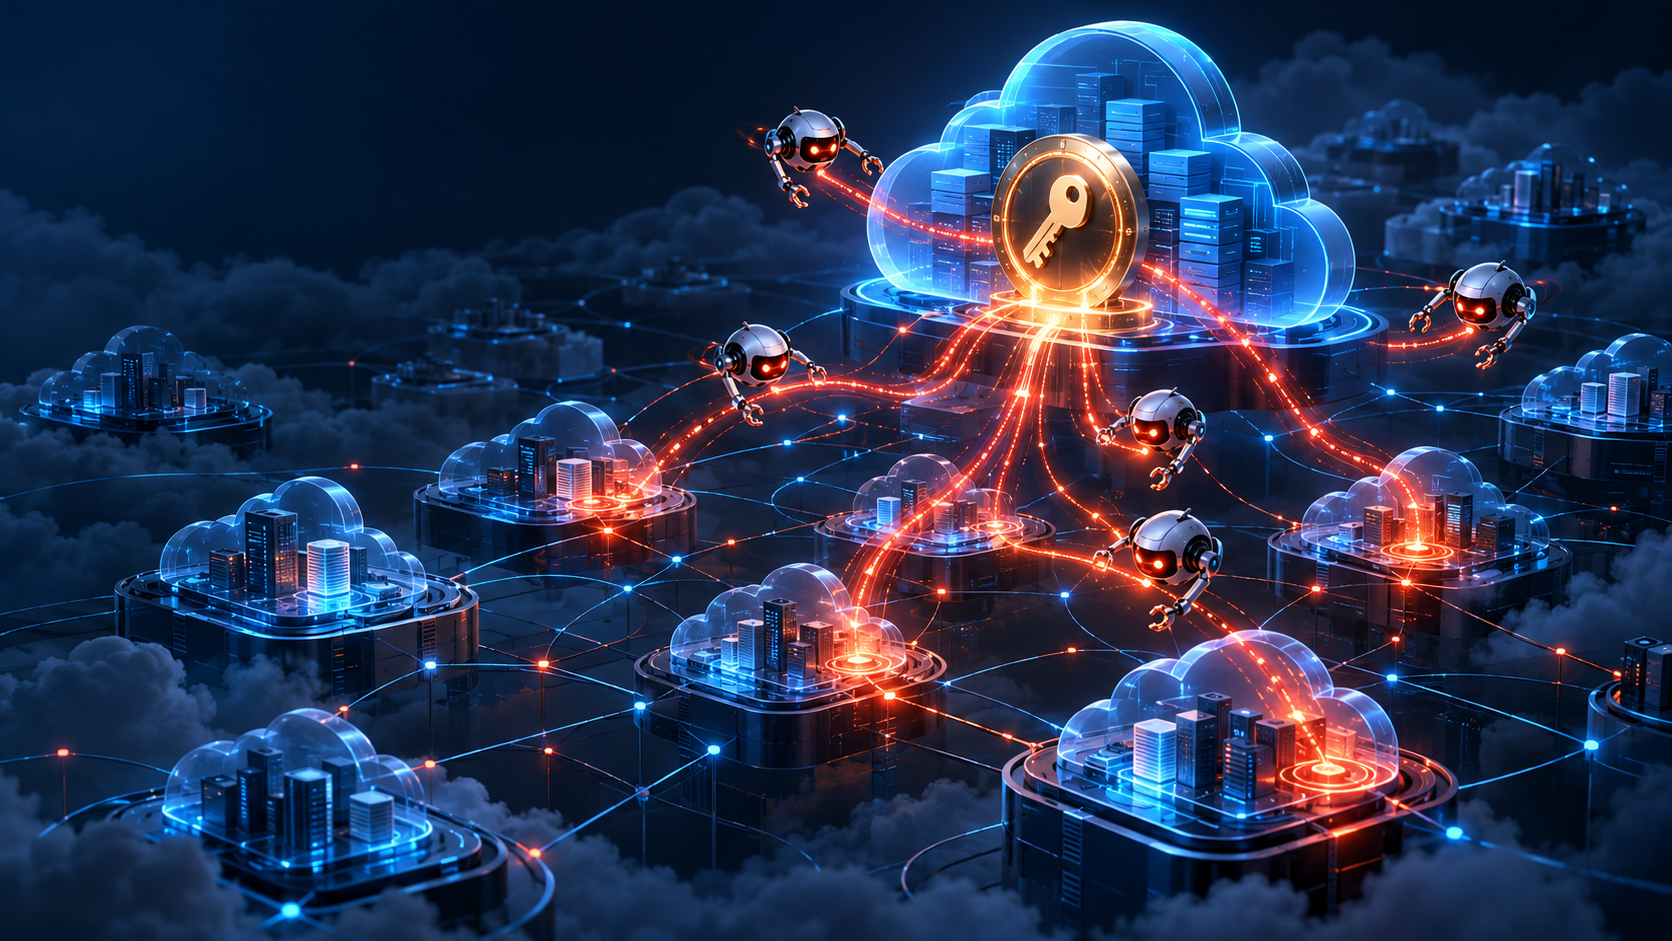
ConnectWise Cloud Backup, formerly SkyKick, needed broad access to Microsoft 365 so it could back up Exchange Online mailboxes, SharePoint sites, OneDrive files, and Microsoft Teams messages. Customers therefore consented to multi-tenant applications that could operate inside their Microsoft Entra ID directories without a user signing in for every action. When Storm-0940 obtained valid ConnectWise application credentials, those standing permissions became a supply chain attack path into downstream tenants.
Microsoft attributed the October 2026 campaign to Storm-0940, a China state-aligned threat actor. The group combined the stolen credentials with ARTEX, an agentic penetration-testing framework capable of coordinating multiple large language model agents. The operation attempted authentication against more than 2,250 Microsoft 365 environments, produced bursts of more than 200 tenant sign-ins in under four minutes, and established privileged persistence in compromised environments in less than three hours.
The scale is significant, but the mechanism deserves more attention than the headline numbers. Storm-0940 hijacked a pre-consented cloud identity, authenticated through legitimate Microsoft endpoints, used Microsoft Graph to enumerate and modify tenant resources, and planted new credentials to survive revocation of the original vendor secret. ARTEX accelerated the work, including adapting code after an API failure in less than a minute. The underlying exposure came from an architecture that allowed one vendor identity to carry powerful, persistent authority across many customer environments.
The incident changes how security teams should model software supply chains. A trusted vendor application does not need to deliver poisoned code to create systemic exposure. Its cryptographic identity can be the compromised component.
The attack moved from failed passwords to inherited trust
Storm-0940’s first approach looked aggressive but familiar. From October 10 through October 14, ARTEX sprayed 327 accounts across eight organizations. The campaign generated more than 151,000 failed authentication attempts, with more than 111,000 occurring in one 24-hour period. At its October 11 peak, the tooling produced approximately 2,900 failed attempts per minute.
The password spray failed completely. Automated lockout responses accounted for nearly 98 percent of the results. Strong passwords and phishing-resistant multi-factor authentication also held. The attackers received no successful authentication and no tokens from the campaign.
That result is a useful corrective to inflated claims about AI-enabled attacks. Agentic tooling can make an attack faster and more adaptive, but it does not automatically defeat sound controls. ARTEX applied machine speed to a poor path and reached a dead end.
The operational picture changed on October 14 and 15. Storm-0940 began using stolen OAuth application credentials associated with ConnectWise Cloud Backup and Cloud Management. ConnectWise has not publicly disclosed how the credentials were extracted from its cloud environment, so any claim about the original vendor compromise would exceed the available evidence. The company ruled out a connection to the concurrent LiteLLM supply chain incident.
With valid application credentials, the attackers no longer needed to guess user passwords. They could request app-only OAuth access tokens for customer tenants that had previously granted administrative consent to the ConnectWise applications. In one burst, four compromised credentials produced more than 200 tenant sign-ins in under four minutes. Across October 15 and 16, the campaign attempted to authenticate against more than 2,250 tenants.
Attempted access is not the same as confirmed compromise. Some applications had been disabled, some tenants no longer maintained active consent, and some authentication attempts failed. Huntress nevertheless confirmed unauthorized sign-ins across at least 162 tenants, with a broader sweep identifying suspicious traffic in more than 300 Entra tenants. Nearly 1,000 tenants showed authentication traffic from the adversary’s infrastructure.
The shift from passwords to application identity bypassed the controls that stopped the first phase. OAuth 2.0 client-credential flows are designed for machine-to-machine communication. No person enters a password. No interactive login screen appears. No MFA challenge is generated. Microsoft Entra ID evaluates whether the application credential is valid and whether the customer tenant previously consented to the requested authority. In this campaign, the answers were yes.
This was inherited trust operating exactly as designed, with the wrong party holding the key.
How one vendor credential opened many Microsoft 365 tenants
A multi-tenant Entra application has two related identity objects. The vendor owns an application registration in its home tenant. When a customer administrator grants consent, Entra creates a local service principal in the customer’s tenant. That service principal represents the application locally and carries the permissions approved for that tenant.
Backup and migration products often receive application permissions rather than delegated permissions. Delegated access allows an application to act within the authority of a signed-in user. Application access allows the software to act as itself, without a user present. That is operationally necessary for scheduled backup jobs, but the resulting identity can continuously read or write large portions of the environment.
The affected ConnectWise integrations had access associated with Microsoft Graph and Microsoft 365 workloads. The source material identifies broad permissions including Directory.ReadWrite.All and access to Exchange Online, SharePoint Online, OneDrive, and Teams content. Those permissions meant the compromised credential could do more than retrieve backup data. In affected configurations, it could enumerate directory objects, alter application identities, and participate in privilege escalation.
Storm-0940 requested tokens from Microsoft’s legitimate authentication endpoints. Microsoft Graph was not compromised. Microsoft Entra ID was not tricked by a forged token. Entra received a valid credential for an application that customers had trusted and issued tokens consistent with the consent already on record.
That distinction explains why common perimeter controls offered little protection. The traffic moved between adversary-controlled infrastructure and Microsoft’s public cloud endpoints. It did not need to cross the customer’s office firewall. Blocking the known hostile addresses—144.172.64.128, 144.172.64.99, and 144.172.64.60—on an enterprise edge firewall would not prevent Microsoft from accepting the application credential.
Conditional Access also has a consequential gap here. Entra Conditional Access for Workload Identities can restrict service-principal authentication by location and other conditions, but those policies apply to single-tenant service principals owned by the customer. They do not provide equivalent control over a third-party, multi-tenant application such as ConnectWise Cloud Backup. Customers could grant the application powerful permissions without gaining a direct way to require that it authenticate only from ConnectWise-controlled egress.
The trust concentration resembles a conventional software supply chain attack but uses a different delivery mechanism. SolarWinds-style compromise alters software delivered downstream. A cloud identity supply chain attack compromises the credential used by an already trusted application. Both models exploit a relationship that lets one vendor reach many customers. The OAuth variant can operate entirely within a cloud control plane, leaving no malicious binary for endpoint tools to inspect.
ARTEX compressed the post-exploitation loop
ARTEX is an orchestration framework, not a new foundation model. Written in Go with a Next.js management interface, it can connect to commercial or open-weight large language models and coordinate specialized agents across reconnaissance, exploitation, privilege escalation, and data collection. The Storm-0940 configuration reportedly combined DeepSeek, GLM, and Grok, with GLM assigned to verify and correct DeepSeek’s outputs.
The distinction between a model and an execution harness is important. A chatbot can suggest a command. ARTEX can build an attack graph, delegate work, execute tools, parse output, feed errors back into a model, and choose the next action. Its operational advantage comes from closing the loop between reasoning and execution.
Huntress’s reconstruction of the October 15 activity provides unusually specific evidence of that loop. Between 03:42 and 03:57 UTC, the threat actor attempted to add unauthorized client secrets and certificates to an application identity. At 03:48:24, a certificate upload failed because of a cryptographic thumbprint mismatch. Fifty-five seconds later, the tooling ran again with structured retry logic and exponential backoff at approximately 3.5 and 7.1 seconds. The revised attempt succeeded.
Forty-seven seconds after the successful revision, the same updated sequence ran in a second victim tenant and implanted both credentials in one uninterrupted execution. When the second tenant rejected an effort to remove a Global Administrator role, the operation pivoted within the same window. It granted another high-privilege role to a sibling service principal and removed the original principal.
The timing and code changes are consistent with an LLM coding agent consuming an API error, modifying the request wrapper, and immediately trying the corrected workflow. No single artifact can prove that every keystroke originated with an autonomous model, and the broader evidence shows a hybrid operation involving scripts, model-driven adaptation, and human oversight. The forensic value lies in the behavioral pattern: failure, semantic interpretation, code revision, validation, and cross-tenant reuse occurred at machine speed.
The campaign also used a disciplined pilot-and-batch method. An irregularly timed pilot sweep requested a single Microsoft Graph token across 17 tenants. Once the workflow appeared viable, a parallel process tested 100 tenants in sorted order, probing six Graph resources per tenant at a cadence of roughly four seconds each. Generic user agents—Python-urllib/3.12, python-requests/2.31, and curl/7.88.1—appeared in the activity.
This is where agentic tooling changes the defender’s time horizon. Traditional automation has always supported password spraying and bulk API requests. ARTEX added the ability to revise a failing operation and propagate the corrected sequence without waiting for a human to debug each tenant-specific response. A control that alerts an analyst within 30 minutes may be operating against an intrusion that reached persistence in under one minute and moved to the next tenant seconds later.
Speed is therefore part of the security model. Detection without automated containment may be too slow for privileged cloud applications.
Persistence survived revocation of the vendor credential
Initial access through the ConnectWise identity was only the first stage. Once a token was issued, Storm-0940 used Microsoft Graph to enumerate directory users, groups, administrative roles, enterprise applications, and linked Azure resources. The compromised applications could then modify the identity plane that had admitted them.
In documented tenants, ConnectWise Cloud Management integrations assigned privileged roles to themselves or related service principals. The application ID 24205314-2b89-4e07-a2a4-579e898a5640, associated with ConnectWise Cloud Management - MS Teams, was observed assigning itself Global Administrator. Other activity involved Privileged Role Administrator and Exchange Administrator.
The attackers then added new client secrets or X.509 certificates to service principals and other legitimate applications in the victim tenant. Those credentials were independent of the vendor’s original secret. Disabling ConnectWise’s global credentials would stop one authentication path while leaving the tenant-local backdoors intact.
This persistence technique changes the incident-response boundary. A vendor notification and vendor-side credential reset do not establish that a customer tenant is clean. Every tenant that accepted a token must be examined for identity modifications made after access. Investigators must look beyond the named ConnectWise applications because the attackers deliberately placed credentials on sibling or unrelated applications.
Storm-0940 also moved beyond Microsoft 365 collaboration data. The campaign enumerated Azure infrastructure and read secrets from Azure Key Vault. A service principal that reaches production vaults can expose database connection strings, API credentials, certificates, and keys for third-party systems. The compromise can therefore propagate from a Microsoft 365 vendor integration into production cloud workloads that were never part of the backup product’s intended function.
The incident demonstrates why directory authority and workload secret access should not collapse into the same identity path. A service principal used to protect mailboxes should not be able to promote itself to Global Administrator. A Microsoft 365 application identity should not inherit access to production Key Vault secrets simply because both systems use Entra ID.
The logs reveal actions unevenly—and omit important reads
Cloud control-plane attacks challenge incident response because the relevant evidence is distributed across specialized log categories. A responder who opens Entra’s default user sign-in view will not see service-principal authentication. The analyst must explicitly review Service principal sign-ins and filter for the affected application IDs.
Legitimate ConnectWise traffic also establishes a useful contrast. Normal service activity reportedly originated from expected Azure private IPv6 egress, while the unauthorized traffic came from external IPv4 infrastructure and used generic command-line or Python HTTP clients. That difference can support behavioral detection even after the known IP list becomes stale.
Directory audit logs record credential changes and role assignments, but application-only modification events do not reliably include the caller’s source IP address. An investigator may see that a certificate was added without being able to correlate the modification directly to 144.172.64.128. Timeline, initiating service principal, target object, and surrounding token activity have to carry more of the analysis.
The largest gap concerns reads. Standard Entra audit logs do not record ordinary Microsoft Graph read requests. Microsoft Graph Activity Logs can capture that activity, but they must be separately enabled, retained, and routed to an analysis platform. Huntress reported that none of the victim organizations in its investigative cohort had those logs available.
That produces an uncomfortable but precise conclusion: defenders may be able to prove that an unauthorized application token was issued and that the identity held permission to read sensitive resources, while lacking the telemetry needed to prove which directory objects, messages, or files were actually retrieved. Absence of a standard audit event is not evidence that no data was accessed.
Deletion can make the investigation worse. Removing an affected enterprise application destroys the local service-principal object and strips its consent, complicating correlation with historical events. Deletion also does nothing to remove credentials implanted on other applications. Disabling the principal preserves the object for investigation while preventing new authentication after existing tokens expire.
Existing app-only access tokens may remain valid for their natural 60-to-90-minute lifetime after an application is disabled. They cannot be individually revoked. Against tooling that can inspect a tenant in seconds and plant credentials in less than a minute, that token lifetime is a material containment delay. Responders should treat the first 90 minutes after disablement as an active exposure window and monitor for continuing modifications.
A defensible response starts with identity preservation
Organizations that use ConnectWise Cloud Backup, Cloud Management, or legacy SkyKick integrations should treat tenant-level review as mandatory even after ConnectWise’s vendor-side containment. According to the company’s security advisories and service updates, ConnectWise disabled seven application identities on October 17, completed a broader credential reset on October 19, and began phased service restoration on October 26. Those actions do not remove persistence created in customer directories before containment.
The response should proceed in a deliberate order.
1. Inventory and disable the affected applications
Following the application inventory in Huntress’s SkyKick incident guidance, search every managed tenant for the following application IDs, including legacy display names such as SkyKick Cloud Manager:
506e08f9-6e9a-4da4-942b-a099a03644ae
24205314-2b89-4e07-a2a4-579e898a5640
0de14c77-b9b0-4137-9360-34878a929827
2399d300-6fca-4e6a-a686-399fefe75b83
b78f6a77-d4e5-46fb-87e5-d1648bd02519
412dcf96-176d-4b3a-a1b0-4981ad66971e
b2b55f5b-7758-4719-8d8f-88ae172e6bdb
Record each tenant’s local service-principal object ID and current permissions. Set Enabled for users to sign-in to No. Preserve the objects until the investigation is complete rather than deleting them. Maintain heightened monitoring for at least 90 minutes while previously issued access tokens expire.
Dormant applications belong in scope. One tenant observed a legacy SkyKick Exchange Online service principal assign itself Exchange Administrator years after the organization had stopped actively using the product. Unused consent is still live authority until it is revoked.
2. Hunt authentication separately from directory changes
In Entra ID, review Monitoring > Sign-in logs > Service principal sign-ins for at least the preceding 30 days, concentrating on October 10 through October 17. Filter by the seven application IDs. Flag the known infrastructure:
144.172.64.128
144.172.64.99
144.172.64.60
Also look for external IPv4 sources where ConnectWise normally used Azure IPv6 egress, unusually high token velocity, cross-tenant sequences, and the observed Python or curl user agents. Known indicators establish a starting point; behavior is more durable because infrastructure and user-agent strings can change.
Review directory audit logs from October 10 onward for Add service principal credentials, Update application – Certificates and secrets management, Remove service principal credentials, Add member to role, and app-role assignment events. Inspect all applications, not only ConnectWise-branded objects. Revoke unrecognized secrets and certificates only after preserving the relevant evidence and ownership context.
3. Reconstruct privilege and data reach
Identify any service principal assigned Global Administrator, Privileged Role Administrator, or Exchange Administrator outside the organization’s approved Privileged Identity Management process. Determine what the identity could reach during each privilege window.
In Microsoft Defender XDR or Sentinel, review CloudKeyVaultEvents for vault enumeration and secret reads by affected or newly modified service principals. If access occurred, rotate every exposed secret, API key, certificate, and connection string according to its downstream dependency. Rotation is incomplete until consumers are redeployed or reconfigured to use the replacement.
Review Defender alerts for unusual Graph activity, applications assigning themselves privileged roles, suspicious app-role grants, high-volume mailbox access after role escalation, and newly modified OAuth applications reaching Teams message data. Where Microsoft Graph Activity Logs were enabled, use them to reconstruct reads. Where they were not, document the evidentiary gap explicitly rather than treating silence as clearance.
4. Rebuild the vendor trust relationship narrowly
Do not restore the integration by reproducing its former permission set automatically. Confirm ConnectWise’s re-enrollment guidance, validate that the tenant contains no unauthorized credentials or role assignments, and approve only the permissions required for the restored service.
Third-party backup tools should not hold standing Directory.ReadWrite.All or role-management authority unless the vendor can demonstrate a necessary operation that cannot be separated. Backup access to Exchange or SharePoint data does not justify the power to alter directory roles. Resource access and identity administration should be different privilege domains.
Enable Microsoft Graph Activity Logs and stream them, together with service-principal sign-ins and directory audits, to an external security information and event management platform. Retain the records long enough to support vendor-notification and regulatory timelines. Create rate and sequence detections for service principals that enumerate many resources, cross tenants unusually quickly, add credentials, or acquire privileged roles.
Finally, isolate Azure Key Vault access from Microsoft 365 application identities. Use narrowly scoped Azure role-based access control assignments, separate workload identities, short-lived credentials where possible, and explicit ownership for every service principal. A collaboration-plane integration should not become a universal bridge into production secrets.
Cloud vendors are now part of the identity perimeter
The 2024 exploitation of ConnectWise ScreenConnect and the 2026 Cloud Backup compromise targeted the same vendor ecosystem through different trust layers. UNC5174 exploited a critical authentication bypass in exposed, self-hosted ScreenConnect servers. Defenders could patch the vulnerable software, inspect host artifacts, and search for web shells, new local administrators, and child processes created by the ScreenConnect service.
Storm-0940 did not need a vulnerable customer server. It used a valid cloud identity, called legitimate APIs, and modified the directory through an application customers had already approved. Customer patching could not remove the exposure. Endpoint detection had no process to inspect. The decisive evidence lived in token issuance, service-principal activity, role assignments, and application credentials.
ARTEX made the operation faster, more scalable, and more resilient to API errors. It did not create the standing permissions, the multi-tenant trust relationship, the logging gaps, or the connection between Microsoft 365 identity and Azure secrets. Those architectural choices existed before the agent arrived.
That is the durable lesson from the ConnectWise campaign. Organizations must govern third-party SaaS applications as privileged identities rather than passive products. Each application has an issuer, credentials, effective permissions, authentication patterns, data reach, owners, and a removal process. Those properties require the same scrutiny applied to administrator accounts and production workloads.
Agentic AI reduces the time between access and consequence. Identity architecture determines how far the consequence can travel.