On September 23, 2026, the FBI acknowledged that a cybercriminal group claimed to have compromised FBIjobs.gov and affected FBI employee personally identifiable information. The agency’s statement was deliberately narrow: the FBI said it was investigating, working with third-party providers, and had not yet determined whether the point of entry was a vendor or the FBI’s own enterprise.
That uncertainty defines the responsible way to analyze the incident. A criminal group identifying itself as ShinyHunters has claimed a much larger breach involving FBI personnel data. Public reporting and the research supplied for this analysis describe an intrusion through Oracle PeopleSoft, lateral movement across application infrastructure, and a pivot into AWS GovCloud. Those details form a technically plausible chain, and parts of the tooling match a PeopleSoft campaign documented months earlier. They are not, however, a public FBI forensic finding.
The confirmed facts are serious enough. Oracle disclosed an unauthenticated, remotely exploitable flaw in PeopleSoft Enterprise PeopleTools on June 10. Google Threat Intelligence Group had already observed ShinyHunters-linked exploitation against PeopleSoft environments before Oracle’s disclosure. Three months later, the FBI was investigating a claimed compromise of the web portal through which it handles recruiting information.
The useful question is therefore larger than whether every attacker claim proves true. How can an exposed enterprise resource planning application become a bridge into systems that were designed to be more trusted than the application itself?
What Is Confirmed—and What Is Still a Claim
The FBI’s public statement confirms three points: a cybercriminal enterprise claimed to compromise FBIjobs.gov; the claimed impact includes employee personally identifiable information; and the FBI had not established the point of breach as of September 23. The statement does not confirm the reported volume of stolen data, the number of affected personnel, the initial-access vulnerability, a pivot into GovCloud, or the full set of systems allegedly reached.
The technical case for PeopleSoft as a suspected entry point comes from the relationship between the portal, the timing, and a previously documented campaign. Oracle’s CVE-2026-35273 security alert identifies a vulnerability in the Updates Environment Management component of PeopleSoft Enterprise PeopleTools 8.61 and 8.62. Oracle scores the flaw at CVSS 9.8. Exploitation requires network access over HTTP, but no credentials or user interaction, and can lead to complete compromise of PeopleTools.
Google Threat Intelligence Group and Mandiant documented active exploitation of this exact component from May 27 through June 9. The observed activity predated Oracle’s advisory, which makes it zero-day exploitation in that campaign. Google attributed the campaign to UNC6240, the cluster associated with ShinyHunters-branded extortion, and identified exposed PeopleSoft Environment Management Hub endpoints as the target.
That reporting validates a campaign-level capability, not its use against the FBI. The supplied research reconstructs the FBI intrusion by mapping the known PeopleSoft campaign onto the alleged breach. Until the FBI, a supporting vendor, or an incident-response firm publishes forensic findings, the exact FBI attack chain should be treated as an informed hypothesis.
The distinction affects how defenders use indicators of compromise. An IP address, executable hash, command, or filename documented in the earlier campaign is a legitimate hunting lead. It is not automatically evidence that the same artifact existed in FBI systems. Threat actors reuse infrastructure and tooling, but they also rotate both. Detection teams should hunt for behaviors and application artifacts alongside exact indicators.
Why CVE-2026-35273 Is an Architectural Problem
PeopleSoft is a multi-tier enterprise platform. A typical deployment includes a browser-facing web tier, PeopleSoft Internet Architecture running on Oracle WebLogic, application servers, process schedulers, integration services, and a database tier. Environment Management exists to discover and administer elements of that estate. Administrative functions that simplify deployment inside a private network become high-value targets when their trust boundary is reachable from the web.
The Pure Internet Architecture trust chain
Oracle’s PeopleSoft architecture documentation describes a request path that begins at the browser, passes through the web server, reaches the application server, and finally produces SQL against the relational database. The Process Scheduler also connects to the database for work that runs outside an interactive browser request. That layout separates presentation, business logic, batch processing, and data storage, but each tier must retain enough connectivity and identity to call the next one.
The web tier is deliberately thin. PeopleSoft servlets receive HTTP requests and relay work to the application tier. Oracle WebLogic commonly hosts both ordinary portal functions and specialized web applications. The relevant distinction is therefore not simply “public website” versus “internal ERP.” A single WebLogic domain can expose multiple application packages with very different purposes and privilege assumptions:
PORTAL.warprovides the primary browser interface.PSIGW.warsupports Integration Broker messaging and cross-system services.PSEMHUB.warsupports Environment Management across PeopleSoft systems.- Other deployed packages provide portlets, monitoring, or legacy integration functions.
An organization may intend to publish only a recruiting portal while unintentionally publishing an administrative or integration route deployed beside it. Reverse proxies and load balancers forward requests by hostname and path, so a neglected URI can cross the same perimeter as the hardened login page. External attack-surface management must enumerate deployed contexts and routes, not merely confirm that the expected homepage requires authentication.
The application tier carries greater authority. PeopleSoft application servers execute PeopleCode business logic, manage transactions, and communicate with the database. Web servers reach them through Oracle Tuxedo and the Jolt protocol. Process Scheduler domains execute batch jobs with their own configuration and database connectivity. A shell on the web tier is therefore valuable partly because it reveals the addresses, ports, service accounts, and configuration needed to approach these more privileged components.
The database boundary also deserves scrutiny. PeopleSoft does not create a separate database login for every browser user. Oracle documents a low-privilege Connect ID, a Symbolic ID that maps a PeopleSoft profile to an access profile, and an Access ID used by the application server to operate against the PeopleSoft schema. The Access ID and password are stored in encrypted form in the PSACCESSPROFILE table. This pooled model reduces database-account administration, but it concentrates authority in the application tier and its configuration.
The normal sign-on path is roughly:
PeopleSoft user
    -> web and application authentication
    -> Connect ID reads the minimum sign-on metadata
    -> Symbolic ID selects an access profile
    -> application tier uses the Access ID for database operations
The Connect ID is intentionally constrained. The Access ID is not. Oracle describes it as the relational database account used when application servers initialize, batch programs connect, and authorized users make applicable two-tier connections. If an attacker reaches the application tier or can query the protected profile data and recover usable access material, the security problem has moved beyond a stolen web session. The attacker is approaching the identity through which the ERP itself reaches its schema.
Segmentation must account for this progression. The public web tier should communicate only with designated application-server endpoints. Jolt listeners should not accept traffic from user networks or arbitrary server segments. Application and batch identities should reach only the required database services. Administrative shares, SSH, and management protocols need separate, explicit policy rather than inheriting access because all hosts belong to the same ERP environment.
Why CVE-2026-35273 Fits a Historical Pattern
CVE-2026-35273 is new, but its shape is familiar. Historical PeopleSoft vulnerabilities have repeatedly appeared where the platform translates between trust domains: browser requests into portal sessions, XML messages into integration actions, Java objects into runtime behavior, filesystem paths into application resources, and web-tier calls into application-tier work.
One of the clearest examples is the historical TokenChpoken attack against PeopleSoft-only single sign-on. Oracle’s current PS_TOKEN documentation explains that the browser-held token includes the user ID, language, issue time, issuing system, and a signature. In password-based deployments, PeopleSoft generates that signature by concatenating the token fields with the local node password and hashing the result with SHA-1.
The architectural weakness is client visibility combined with a shared secret. The browser possesses the token fields and the resulting signature. Historical TokenChpoken research showed that an attacker who obtained a low-privilege token could perform an offline password-guessing attack against the node password. The target would see no stream of failed logins because the computational work occurred on attacker-controlled hardware. If the node password was recovered, the attacker could alter the user ID, recompute the signature, and present a forged token as a more privileged user. Trusted PeopleSoft nodes sharing that secret could broaden the impact.
TokenChpoken does not explain the 2026 exploit, and modern deployments may use stronger external identity controls or certificate-based token signing. Its relevance is architectural. A mechanism built to let connected PeopleSoft nodes trust one another turned one exposed token and one shared secret into a cross-node authentication problem. CVE-2026-35273 similarly appears at an integration seam where the platform accepts that a request reaching an internal management function has already earned trust.
Deserialization flaws provide another precedent. Java applications often serialize an object into bytes for storage or transport, then deserialize those bytes to rebuild the object. Unsafe deserialization lets attacker-controlled input select classes and trigger methods during reconstruction. Oracle’s October 2017 Critical Patch Update records CVE-2017-10366 as a CVSS 9.8, remotely exploitable, unauthenticated flaw in the PeopleTools Performance Monitor component. Subsequent public exploit research described an operating-system command-execution path.
Java now provides controls that can reduce generic deserialization risk. JEP 290 introduced filters that can reject unexpected classes and constrain object-graph depth, reference count, array size, and stream size before deserialization completes. JEP 415 later added context-specific filter factories so different deserialization sites can apply different policies. These controls are valuable when a component uses Java object serialization. They do not automatically secure every parser, and they do not replace Oracle’s product patches. The suspected 2026 chain involves XML decoding behavior and application routing, so defenders should avoid treating one JVM-wide reject list as a universal cure.
Oracle describes CVE-2026-35273 as an unauthenticated network vulnerability in Updates Environment Management. The vendor does not publish the exploit chain in its alert. The supplied research and campaign analysis identify the relevant surface as the PeopleSoft Environment Management Hub, or PSEMHUB, and the PeopleSoft Integration Gateway listener.
The central failure is misplaced trust. An internal management endpoint may assume that a request reaching it has already passed authentication and filtering upstream. That assumption only holds if every route into the endpoint enforces the same controls. A public integration component that can cause a server-side request to an internal endpoint collapses the boundary.
Server-side request forgery (SSRF) exploits this condition. The attacker does not connect directly to an internal-only service. Instead, the attacker sends a crafted request to a public service and induces that service to make a second request. The internal service sees a connection from a trusted application host or loopback interface, not from the attacker’s external address.
The suspected chain adds unsafe Java deserialization. Java’s XMLDecoder can reconstruct objects and invoke methods described by XML. When attacker-controlled XML reaches a decoder without a strict allowlist and safe parsing model, the input can become executable behavior rather than inert configuration data. SSRF supplies the route; unsafe deserialization supplies code execution.
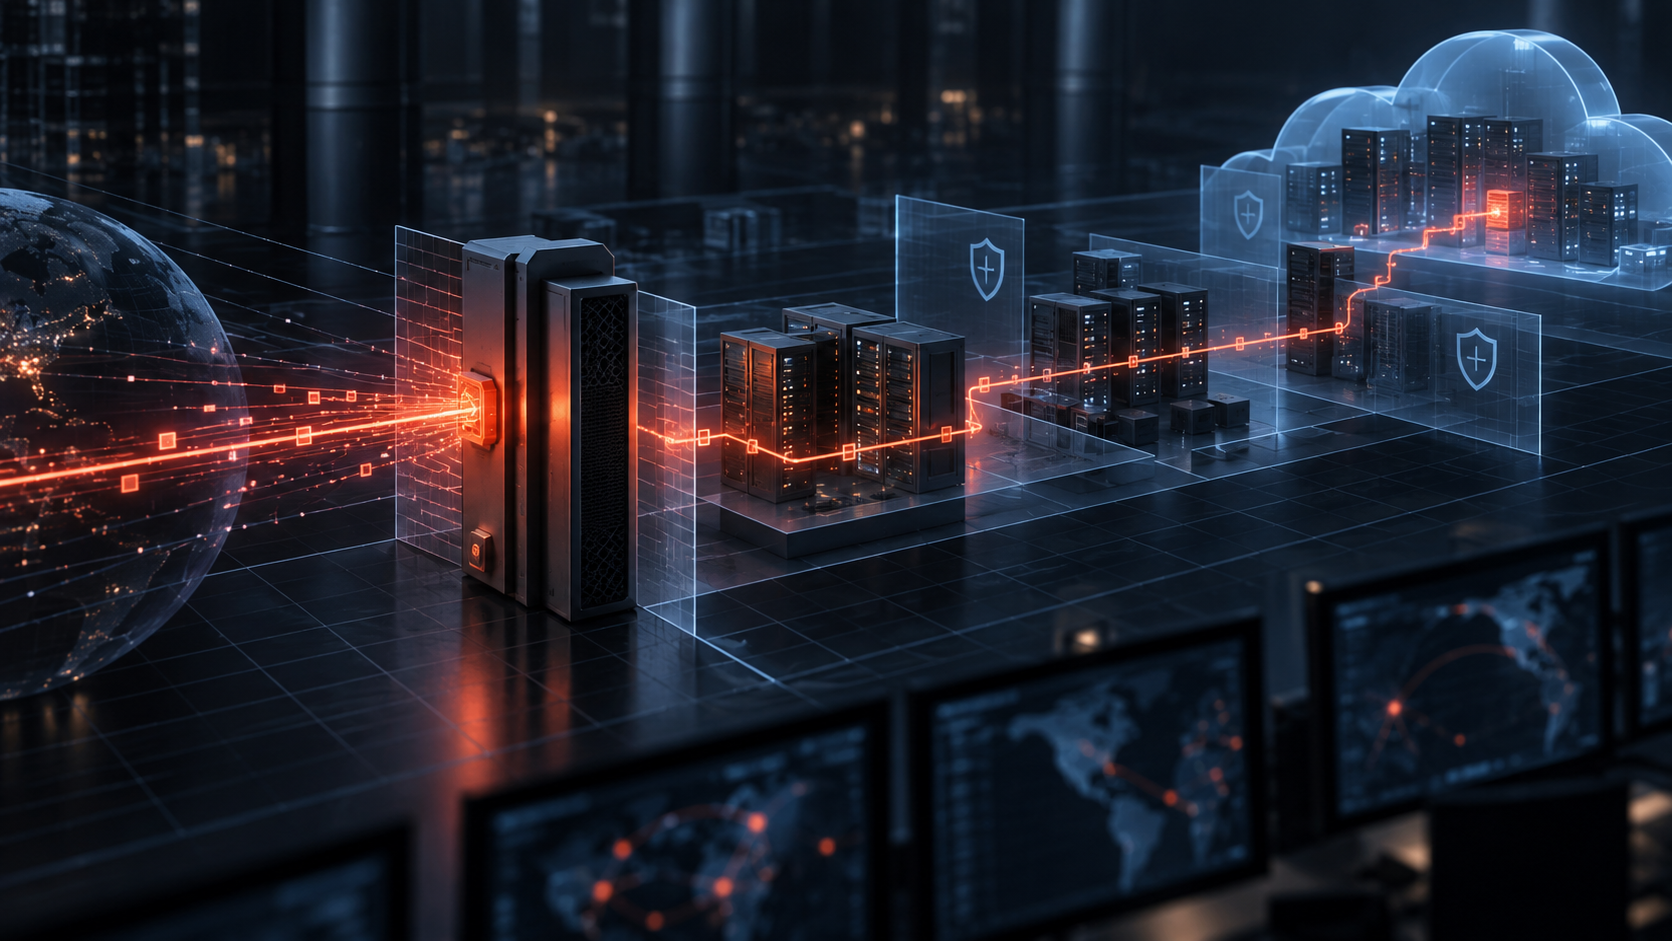
Conceptually, the path is:
Internet attacker
    -> public PeopleSoft integration endpoint
    -> server-side request to an internal PSEMHUB endpoint
    -> unsafe decoding of attacker-controlled XML
    -> command execution in the PeopleSoft service context
Remote code execution initially provides the privileges of the compromised service account, not control of every connected system. The blast radius depends on what that account can read, which hosts it can reach, which credentials are stored locally, and which trust relationships exist between tiers. Those secondary conditions turn a serious application exploit into an enterprise breach.
The dependence on downstream controls explains why a Web Application Firewall cannot be the entire answer. A WAF may block known request patterns or prevent access to specific URI paths. It cannot repair an application architecture that authorizes requests based on where they originated. The durable fix combines Oracle’s patch or mitigation with endpoint isolation, server-side authorization, minimal service-account privileges, and segmentation between the public web tier and management functions.
From Web-Tier Execution to Persistent Access
The earlier PeopleSoft campaign provides a concrete model for what an attacker can do after execution. Google’s investigation found five sequential staging addresses hosting Python HTTP servers on port 8888. The exposed directories contained customized MeshCentral agents, attacker shell history, and a propagation script named with a victim-specific prefix followed by _fanout.sh.
MeshCentral is a legitimate remote-management platform. That legitimacy is useful to an intruder. Remote monitoring and management software provides durable command execution, file transfer, and host administration while resembling software an operations team might deploy. The campaign’s Windows agents were configured to connect over encrypted WebSockets to azurenetfiles[.]net, a name chosen to resemble a legitimate Azure service.
This technique does not defeat encryption; it exploits the assumptions surrounding encrypted traffic. TLS protects content in transit, but it also prevents ordinary network devices from inspecting that content. A plausible domain, port 443, and a valid certificate can make command-and-control traffic look routine unless defenders correlate DNS age, destination reputation, process ancestry, and which binary opened the connection.
The documented campaign also shows why detection based only on malware signatures underperforms. MeshCentral itself is not malware. Python’s HTTP server, npm, SSH, grep, and zstd are ordinary tools. The malicious signal emerges from context:
- An application server installs remote-management software outside an approved deployment workflow.
- A PeopleSoft service launches a shell or package manager.
- A new binary establishes a persistent WebSocket connection to a recently observed external domain.
- An application host reads internal host maps, mount tables, or configuration files unrelated to normal request processing.
- A web tier initiates SSH connections across an internal server range.
These are behavior chains, not isolated indicators. Endpoint detection and response controls need visibility into the PeopleSoft and WebLogic tiers, even when those systems are treated as fragile legacy infrastructure. Excluding an ERP server from monitoring because an agent might affect performance trades a measurable operational concern for a major forensic blind spot.
The supplied research describes attackers inspecting psappsrv.cfg, /etc/hosts, mounted filesystems, and WebLogic config.xml files. Google observed comparable reconnaissance in the wider PeopleSoft campaign. Those files can reveal database endpoints, application topology, service identities, and shared storage. A service account that legitimately needs to read its own configuration can therefore become a discovery mechanism after compromise.
The campaign’s fanout script then automated SSH authentication attempts against internal hosts using common application and administrative accounts. It also attempted to use existing SSH trust relationships. This is the point where old operational conveniences become security liabilities. Shared passwords, reusable keys, broad known_hosts relationships, and unrestricted east-west SSH access allow one compromised tier to interrogate the next.
Defenders should expect an attacker to automate this stage. A web-tier compromise no longer produces a leisurely sequence of manual commands. Scripts can parse local configuration, identify naming conventions, test credentials, deploy remote agents, and collect data in minutes. Containment decisions and credential revocation must be designed for machine-speed propagation.
The Alleged GovCloud Pivot and the Identity Boundary
The most consequential part of the supplied reconstruction is the alleged movement from PeopleSoft infrastructure into AWS GovCloud. Public evidence has not yet confirmed that pivot in the FBI incident. The scenario nevertheless exposes a familiar hybrid-cloud failure mode: an internet-facing application carries credentials that are more trusted than the host on which they reside.
AWS GovCloud operates as an isolated AWS partition with two regions and accounts separate from the standard AWS partition. That separation does not make valid credentials harmless. If an on-premises application requires programmatic access to a cloud service, the application needs some form of identity. A long-lived access key stored in a configuration file can be copied and replayed from another system unless additional controls bind its use to an expected context.
The dangerous architecture looks like this:
Public web tier
    -> locally stored cloud credential
    -> broad IAM permissions
    -> network route to sensitive cloud APIs
    -> data stores outside the web tier's intended function
Each arrow represents a separate control decision. The initial exploit only compromises the web tier. Local secret storage converts host access into an identity compromise. Broad Identity and Access Management (IAM) permissions expand that identity’s authority. Permissive network and resource policies let the stolen identity operate from an unexpected location. Excessive data access converts the identity compromise into collection and exfiltration.
The correct design removes as many arrows as possible. Hybrid workloads should prefer short-lived credentials obtained through workload identity federation or another brokered mechanism over static access keys. The cloud role should permit only the API actions and resources necessary for the application’s current function. Resource policies should restrict access through designated private paths or known network contexts. High-value datasets should sit behind a separate authorization layer rather than inheriting trust from a portal integration.
Credential rotation is necessary after suspected compromise, but rotation does not answer whether the key was used. Incident responders need cloud control-plane logs, data-access logs, network flow records, and application telemetry with synchronized timestamps. They should examine role assumptions, API calls from unusual addresses, enumeration activity, bulk reads, snapshot creation, and changes to logging or IAM policy. A stolen credential may produce perfectly valid authentication records; the anomaly is in its origin, sequence, and scope.
The same principle applies outside AWS. Cloud security fails when identity is treated as proof of legitimacy rather than one input to an authorization decision. A valid credential presented from a compromised legacy host is still a valid credential. Context-aware policy, least privilege, and independent data-plane controls limit what that credential can accomplish.
Patching Is a Containment Decision, Not Calendar Hygiene
Oracle published its alert on June 10 and urged immediate action. The FBI acknowledged the claimed portal compromise on September 23. If CVE-2026-35273 proves to be the entry point, the elapsed time will raise a critical question: why did an internet-facing system remain exposed to an unauthenticated takeover vulnerability after a patch and mitigations were available?
Legacy ERP patching is operationally difficult. PeopleSoft estates often contain custom components, brittle integrations, specialized batch processes, and narrow maintenance windows. A rushed update can interrupt recruiting, payroll, finance, or student operations. Those constraints are real, but they do not change the exposure created by a remotely exploitable flaw.
When a critical application cannot be patched immediately, the decision is not simply “patch now” versus “accept risk.” Defenders can disable the vulnerable service, remove an unused component, restrict the affected paths, place the application behind authenticated access, or temporarily take the exposed function offline. Google’s campaign guidance recommends disabling the Environment Management Hub where possible, removing PSEMHUB in applicable single-server deployments, or blocking external access to /PSEMHUB/* and /PSIGW/HttpListeningConnector when the service cannot be disabled.
Patching also does not evict an attacker who arrived first. Because exploitation occurred before Oracle’s advisory in the wider campaign, any exposed environment must be evaluated for pre-patch compromise. Applying the update closes the entry path; it does not remove remote-management agents, web shells, added keys, stolen secrets, or persistence on adjacent hosts.
A defensible response sequence is:
- Isolate or block the vulnerable surface while preserving volatile evidence.
- Capture relevant application, operating-system, identity, network, and cloud logs.
- Hunt for exploitation and persistence across the full period of exposure.
- Patch or remove the affected PeopleSoft component.
- Rotate credentials accessible to the compromised service and revoke active sessions.
- Validate segmentation and authorization before restoring external access.
Google’s published hunting guidance is unusually specific. Teams should review PeopleSoft Internet Architecture WebLogic access logs for external POST requests to /PSEMHUB/hub and /PSIGW/HttpListeningConnector. They should inspect the PSEMHUB web application for unauthorized JSP files and unexpected content under environment-management transaction and storage directories. Network teams should review outbound traffic from PeopleSoft hosts, including SMB, SSH, HTTP, and persistent WebSocket connections to untrusted destinations.
Exact indicators from the campaign remain useful, including the azurenetfiles[.]net domain, the sequential staging addresses 142.11.200.186 through 142.11.200.190, and the README-IF-YOU-SEE-THIS-YOUVE-BEEN-HACKED.TXT marker. Organizations should consume current indicators from the source investigation rather than copy a static list into permanent policy. Behavioral detections survive infrastructure changes better than a blocklist alone.
The Control Lessons for Hybrid Enterprise Systems
The FBI Jobs incident is still developing, but the control lessons do not depend on the final attribution or the exact volume of data involved.
First, management planes cannot inherit trust from network location. Administrative servlets, integration listeners, deployment hubs, metadata services, and orchestration APIs require explicit authentication and authorization at the service boundary. A reverse proxy and an access control list are supplemental controls, not substitutes for application-layer enforcement.
For PeopleSoft, that principle starts with an inventory of every deployed web application, servlet context, Integration Broker listener, Environment Management component, Jolt endpoint, Process Scheduler domain, and database access profile. Teams should compare what is installed against what the business actually uses. Unneeded contexts should be removed or disabled. Required administrative contexts should be reachable only through a controlled management path, and externally required portals should receive explicit route allowlists rather than broad publication of an entire WebLogic domain.
Second, internet exposure must be continuously inventoried. The PeopleSoft campaign began with exposed Environment Management endpoints that organizations often did not realize were reachable. Asset inventories built from procurement records or configuration databases drift from reality. External attack-surface discovery should verify what an unauthenticated party can actually reach, then map those services to owners, versions, data classifications, and remediation authority.
Third, the public tier should be architected as disposable and untrusted. It should not contain reusable administrative credentials, unrestricted SSH keys, or configuration secrets that unlock broader environments. A compromised front end should encounter tightly scoped identities, deny-by-default east-west rules, and data services that independently enforce authorization.
PeopleSoft-only single sign-on also deserves a deliberate review. Organizations using password-signed PS_TOKEN cookies should assess node-password length, rotation, distribution, and the number of systems that trust each issuing node. Certificate-based PS_TOKEN signing removes the shared node password from token signing. External identity federation can remove the same dependency only when the resulting architecture no longer relies on password-signed PeopleSoft-only tokens for downstream SSO. Any migration must preserve authorization boundaries rather than create one broadly trusted identity plane. Existing tokens and secrets should be invalidated when a node is suspected of compromise.
Fourth, monitoring coverage must include legacy systems. An environment that cannot tolerate an endpoint agent still needs compensating telemetry: process accounting, application access logs, file-integrity monitoring, centralized authentication logs, outbound network controls, and protected audit storage. “Too critical to monitor” usually means too critical to reconstruct after a breach.
Java runtime hardening belongs in the same program. Where PeopleSoft or a supporting WebLogic application uses Java serialization, administrators should validate the vendor-supported JDK level and test an allowlist-oriented jdk.serialFilter policy in a representative environment. Filters should impose graph and stream limits as well as class restrictions. Because an overly broad filter preserves gadget-chain exposure and an overly narrow filter can break production workflows, deployment requires application-aware testing and observable failure logging.
Finally, remediation authority must match the speed of exploitation. A vulnerability with network access, no authentication requirement, low complexity, and total confidentiality, integrity, and availability impact is an emergency operating condition. The team accountable for the service needs preapproved options to patch, isolate, disable, or shut down the exposed function. Escalation paths that require days of meetings are themselves part of the attack surface.
The alleged FBI breach is compelling because of the institution involved. The architecture behind it is ordinary: a legacy application at the edge, internal services built on implicit trust, operational credentials on the host, and a high-value cloud environment downstream. That combination exists in universities, hospitals, governments, and large enterprises everywhere.
Cloud isolation and product patching are only part of the defense. Security boundaries ultimately depend on the identities and integrations crossing them. An exposed application becomes a bridge when downstream systems grant its location, credentials, or role more trust than its compromise potential justifies.